

SAP Security Notes Review: February 2022
08 February 2022


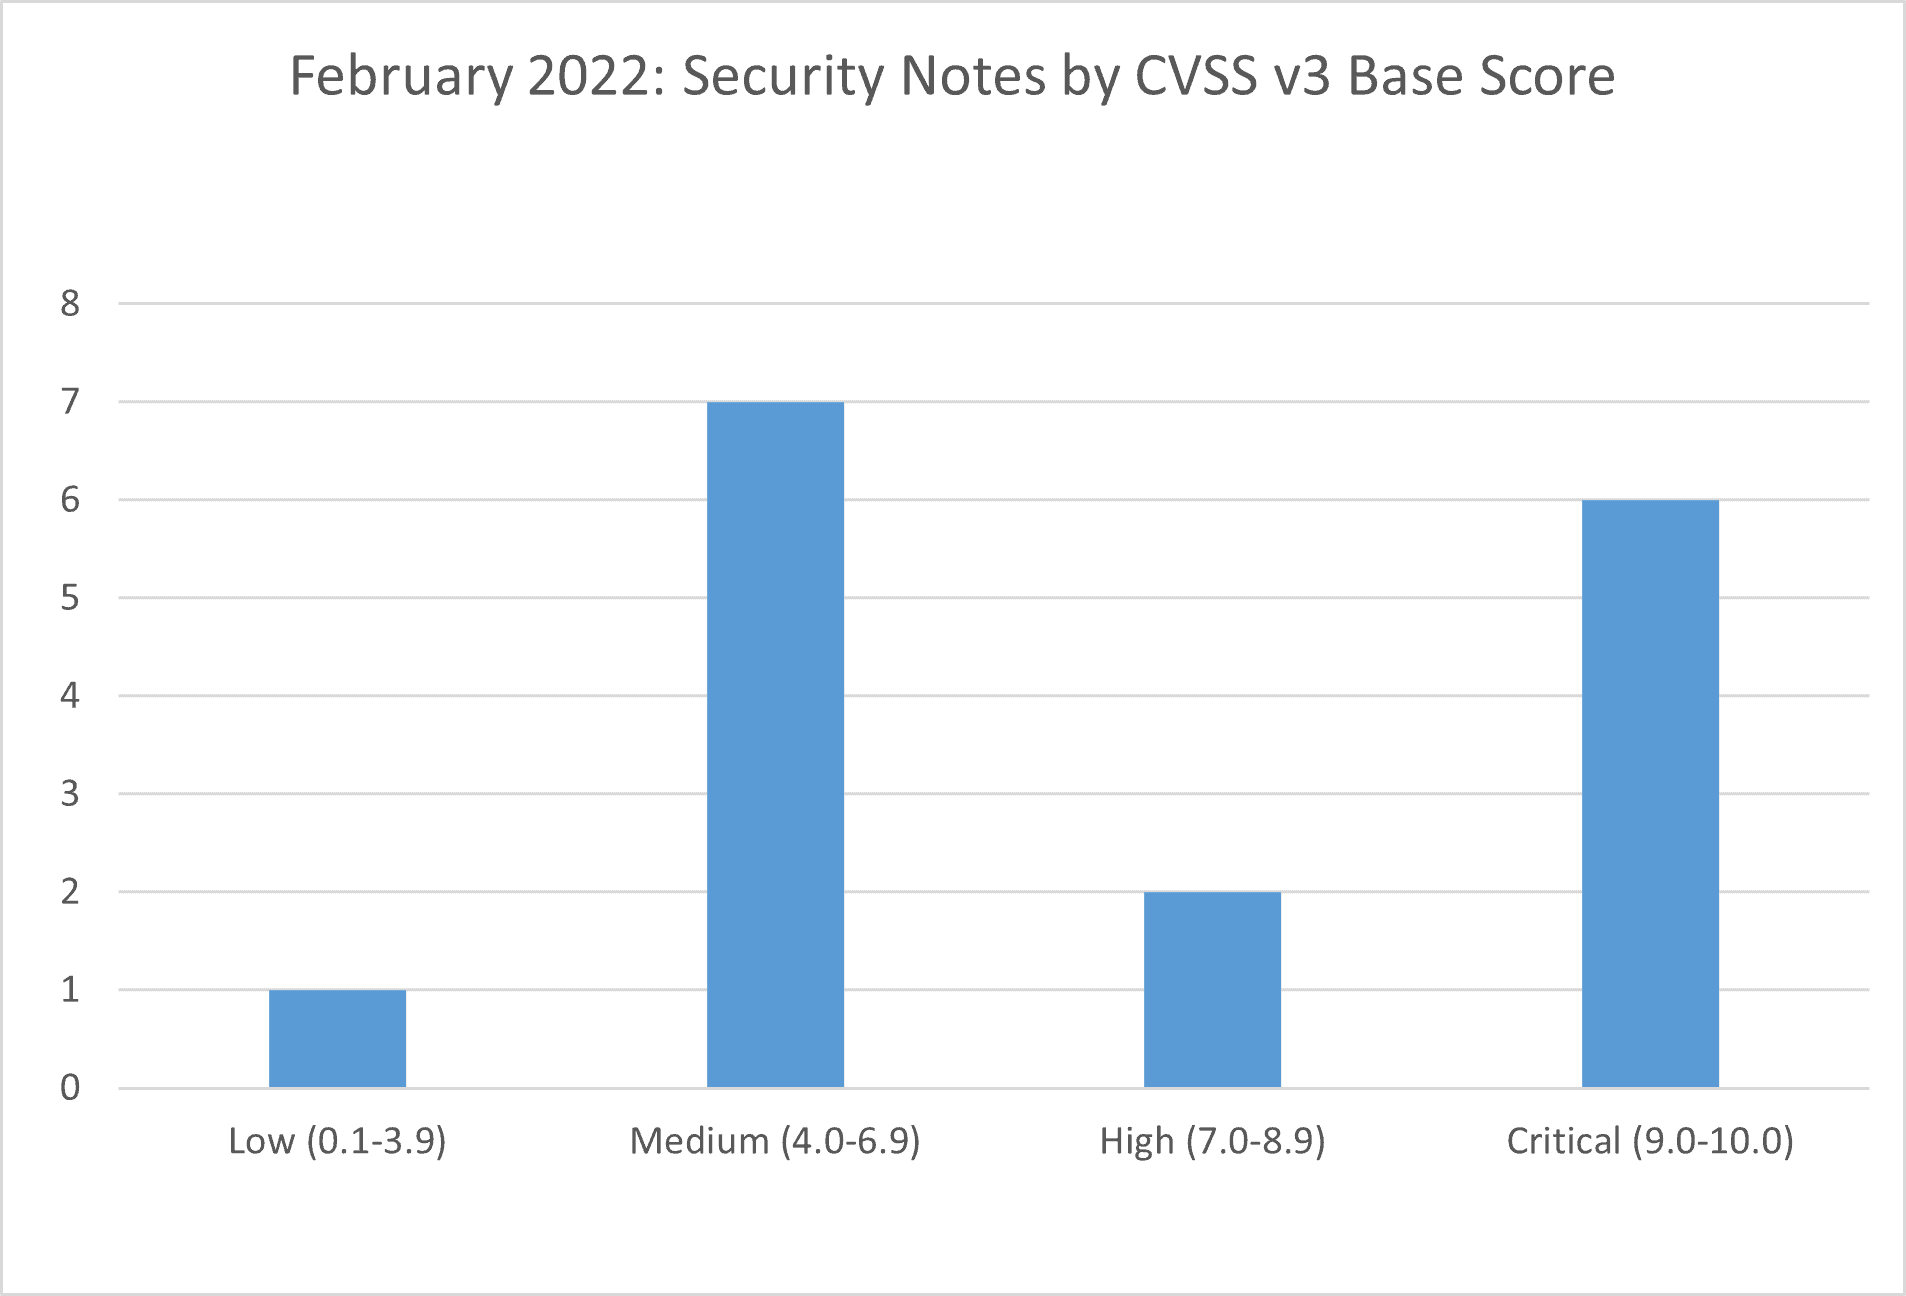
SAP’s security patch day for February 2022 has seen the release of 16 new OSS SAP security notes. 1 note has been classified as low, 7 notes have been classified as medium, 2 as high and 6 as critical, based on CVSS v3.0 Rating.
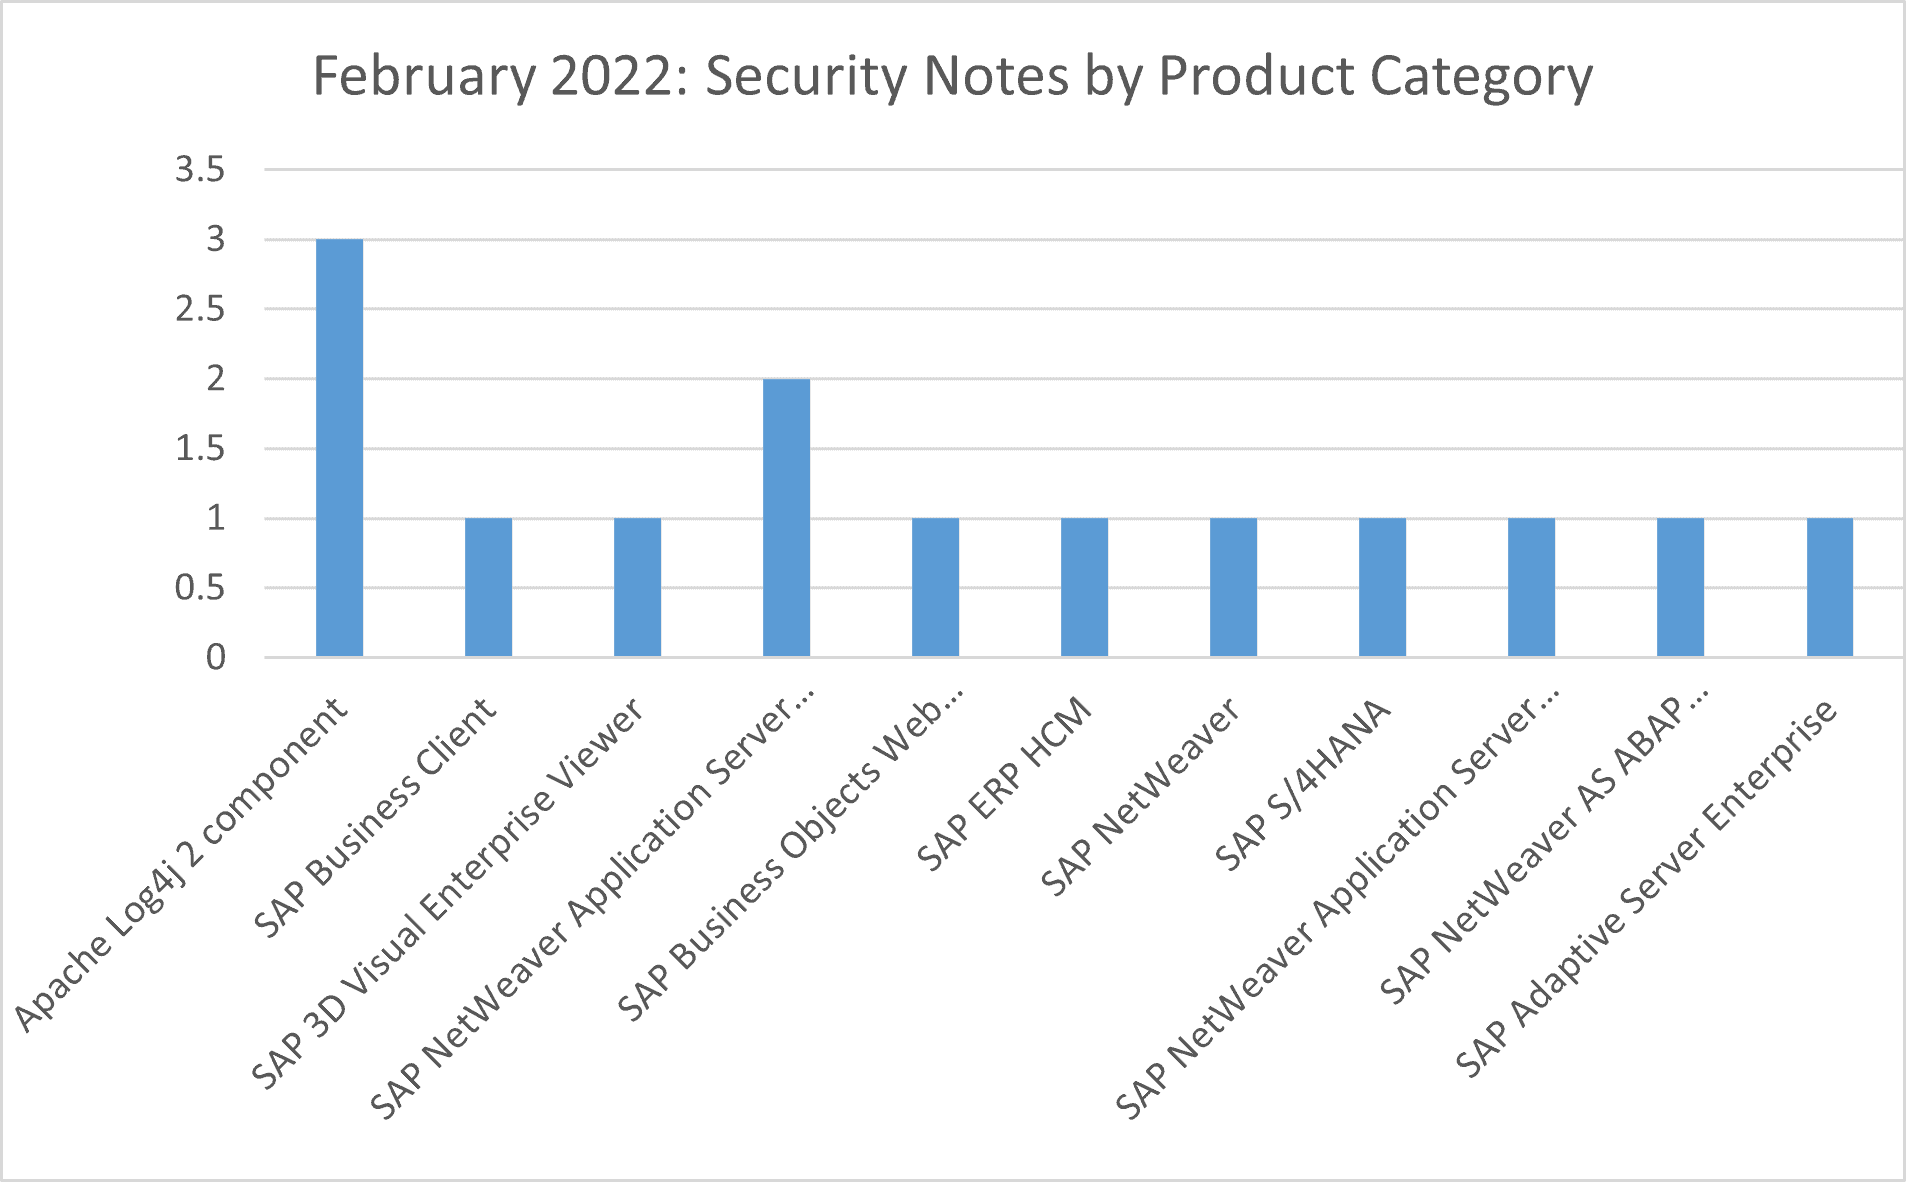
3 notes have been released for Apache Log4j 2 component and 2 for SAP NetWeaver Application Server ABAP and ABAP Platform. Single notes have been released for SAP Business Client, SAP 3D Visual Enterprise Viewer, SAP Business Objects Web Intelligence, SAP ERP HCM, SAP NetWeaver, SAP S/4HANA, SAP NetWeaver Application Server Java, SAP NetWeaver AS ABAP (Workplace Server) and SAP Adaptive Server Enterprise.
Vulnerabilities: February 2022 Highlights
[CVE-2022-22536] Request smuggling and request concatenation in SAP NetWeaver, SAP Content Server and SAP Web Dispatcher (SAP Note 3123396)
SAP NetWeaver Application Server ABAP, SAP NetWeaver Application Server Java, ABAP Platform, SAP Content Server 7.53 and SAP Web Dispatcher are vulnerable for request smuggling and request concatenation.
An unauthenticated attacker can prepend a victim’s request with arbitrary data. This way, the attacker can execute functions impersonating the victim or poison intermediary Web caches. A successful attack could result in complete compromise of Confidentiality, Integrity and Availability of the system.
[CVE-2022-22540] SQL Injection vulnerability in SAP NetWeaver AS ABAP (Workplace Server) (SAP Note 3140587)
SAP NetWeaver AS ABAP (Workplace Server) allows an attacker to execute crafted database queries, that could expose the backend database. A successful attack could result in disclosure of table of contents from the system, but no risk of modification is possible.
[CVE-2022-22534] Cross-Site Scripting (XSS) vulnerability in SAP NetWeaver (SAP Note 3124994)
Due to insufficient encoding of user input, SAP NetWeaver allows an unauthenticated attacker to inject code that may expose sensitive data like user ID and password. These endpoints are normally exposed over the network and successful exploitation can partially impact confidentiality of the application.