

SAP Security Notes Review: February 2023
14 February 2023


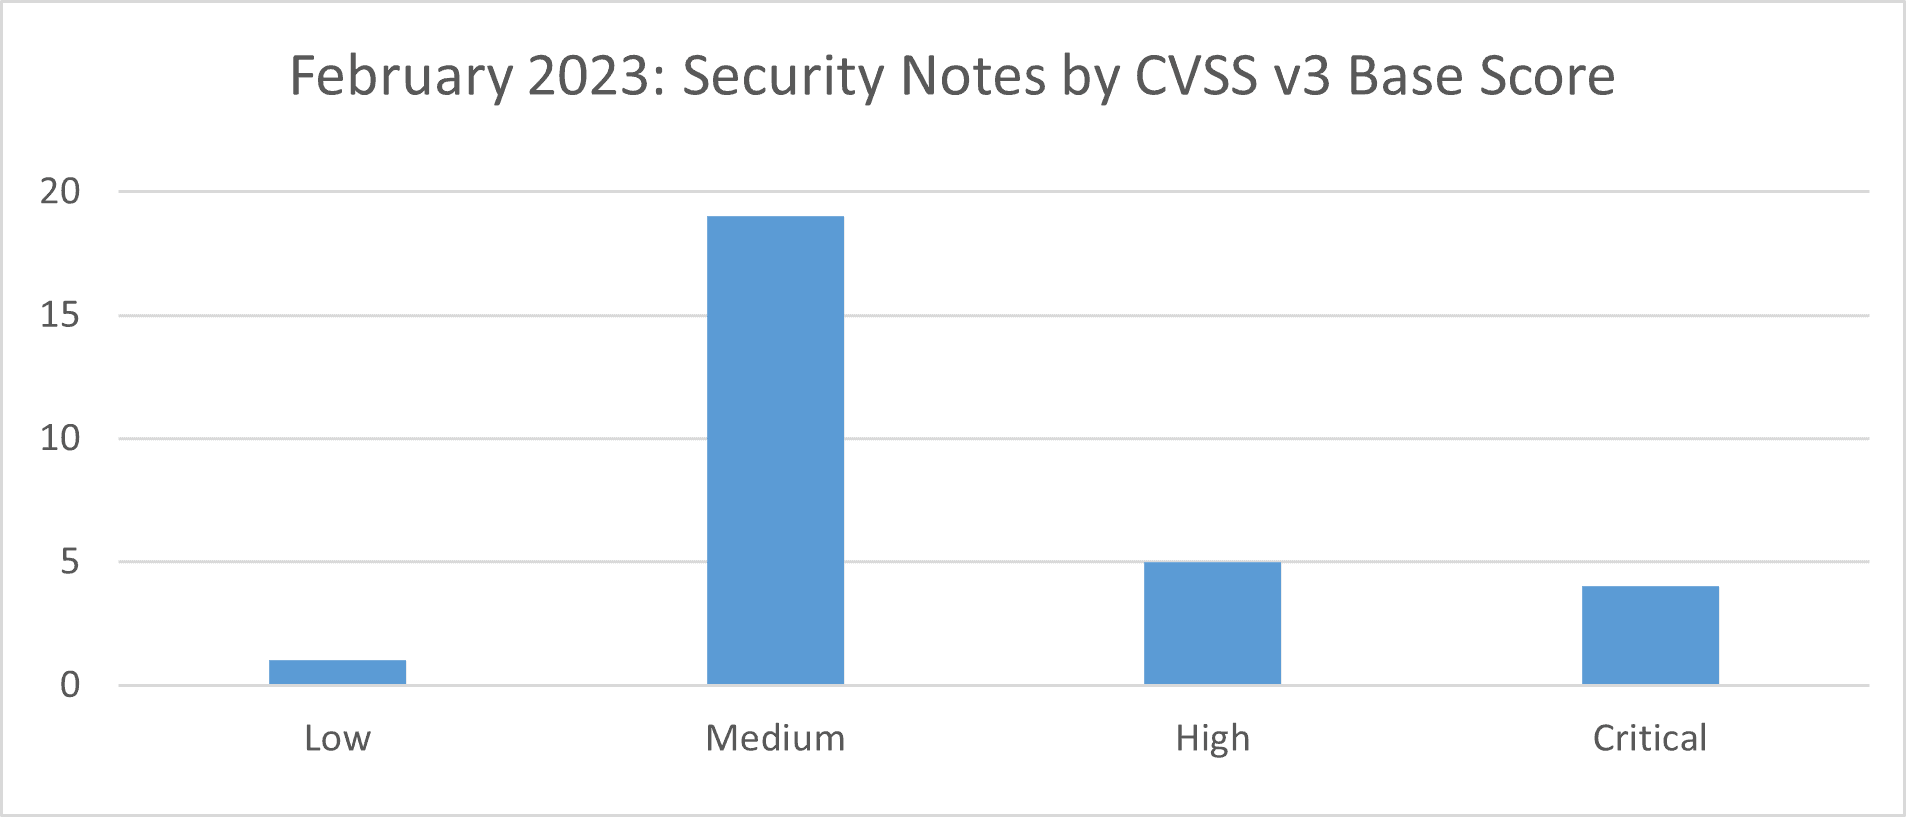
SAP’s security patch day for February 2023 has seen the release of 25 new and 4 updated OSS SAP security notes. 4 notes have been classified as critical, 5 as high, 19 as medium and 1 as low based on CVSS v3.0 Rating.
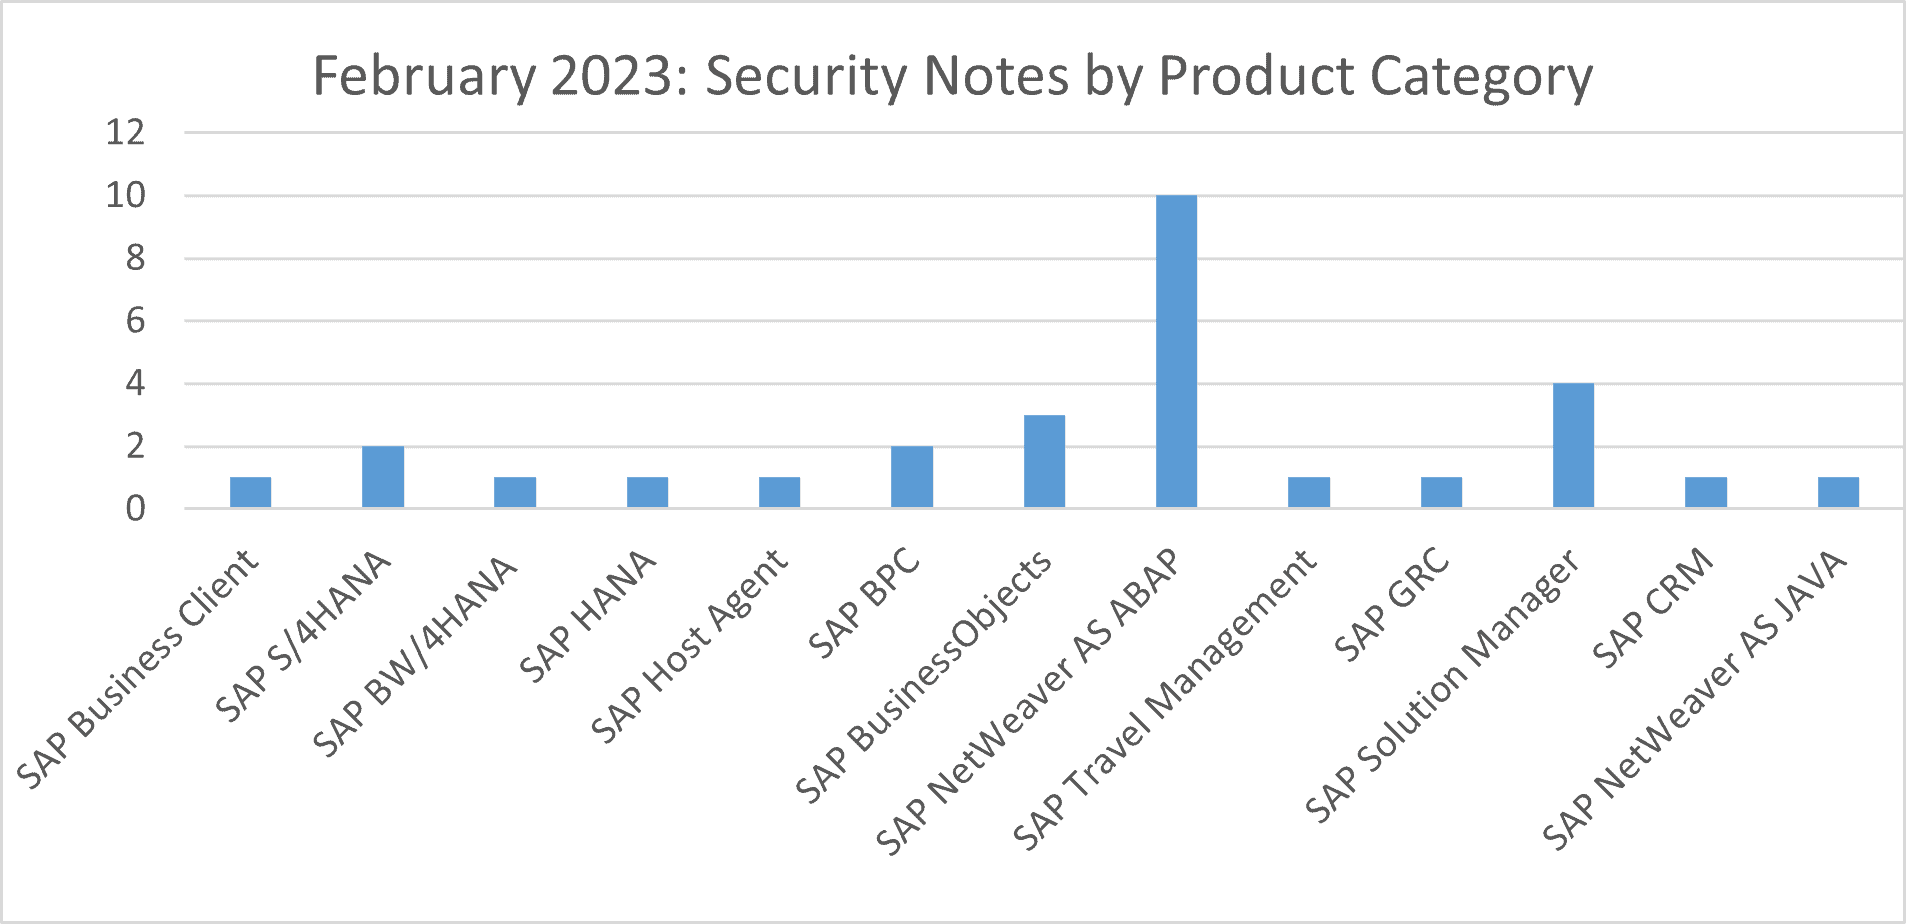
10 notes have been released for SAP NetWeaver AS ABAP, 4 notes for SAP Solution Manager, 3 notes for SAP BusinessObjects, 2 notes for SAP BPC and 2 for SAP S/4HANA. Single notes have been released for SAP Business Client, SAP BW/4HANA, SAP HANA, SAP Host Agent, SAP Travel Management, SAP GRC, SAP CRM and SAP NetWeaver AS JAVA.
Vulnerabilities: February 2023 Highlights
[CVE-2023-24523] Privilege Escalation vulnerability in SAP Host Agent (Start Service) (SAP Note 3285757)
An attacker can use a non-admin user to submit a specially crafted webservice request with an operating system command which will be executed with administrator privileges. The OS command can read or modify any user or system data and can make the system unavailable.
[CVE-2023-0020] Information disclosure vulnerability in SAP BusinessObjects Business Intelligence platform (SAP Note 3263135)
SAP BusinessObjects Business Intelligence platform allows an authenticated attacker to access sensitive information which is otherwise restricted.
[CVE-2023-24530] Unrestricted Upload of File in SAP BusinessObjects Business Intelligence Platform (CMC) (SAP Note 3256787)
SAP BusinessObjects Business Intelligence Platform (CMC) allows an authenticated admin user to upload malicious code that can be executed by the application over the network. On successful exploitation, attacker can perform operations that may completely compromise the application causing high impact on confidentiality, integrity and availability of the application.
[CVE-2023-23858] Cross-Site Scripting (XSS) vulnerability in SAP NetWeaver AS for ABAP and ABAP Platform (SAP Note 3293786)
Due to insufficient input validation, SAP NetWeaver AS for ABAP and ABAP platform allows an unauthenticated attacker to send a crafted URL to a user. By clicking this URL the user could be directed out-side of SAP and give away sensitive data.