SAP Security Notes Review: July 2023
23 April 2023


Overview
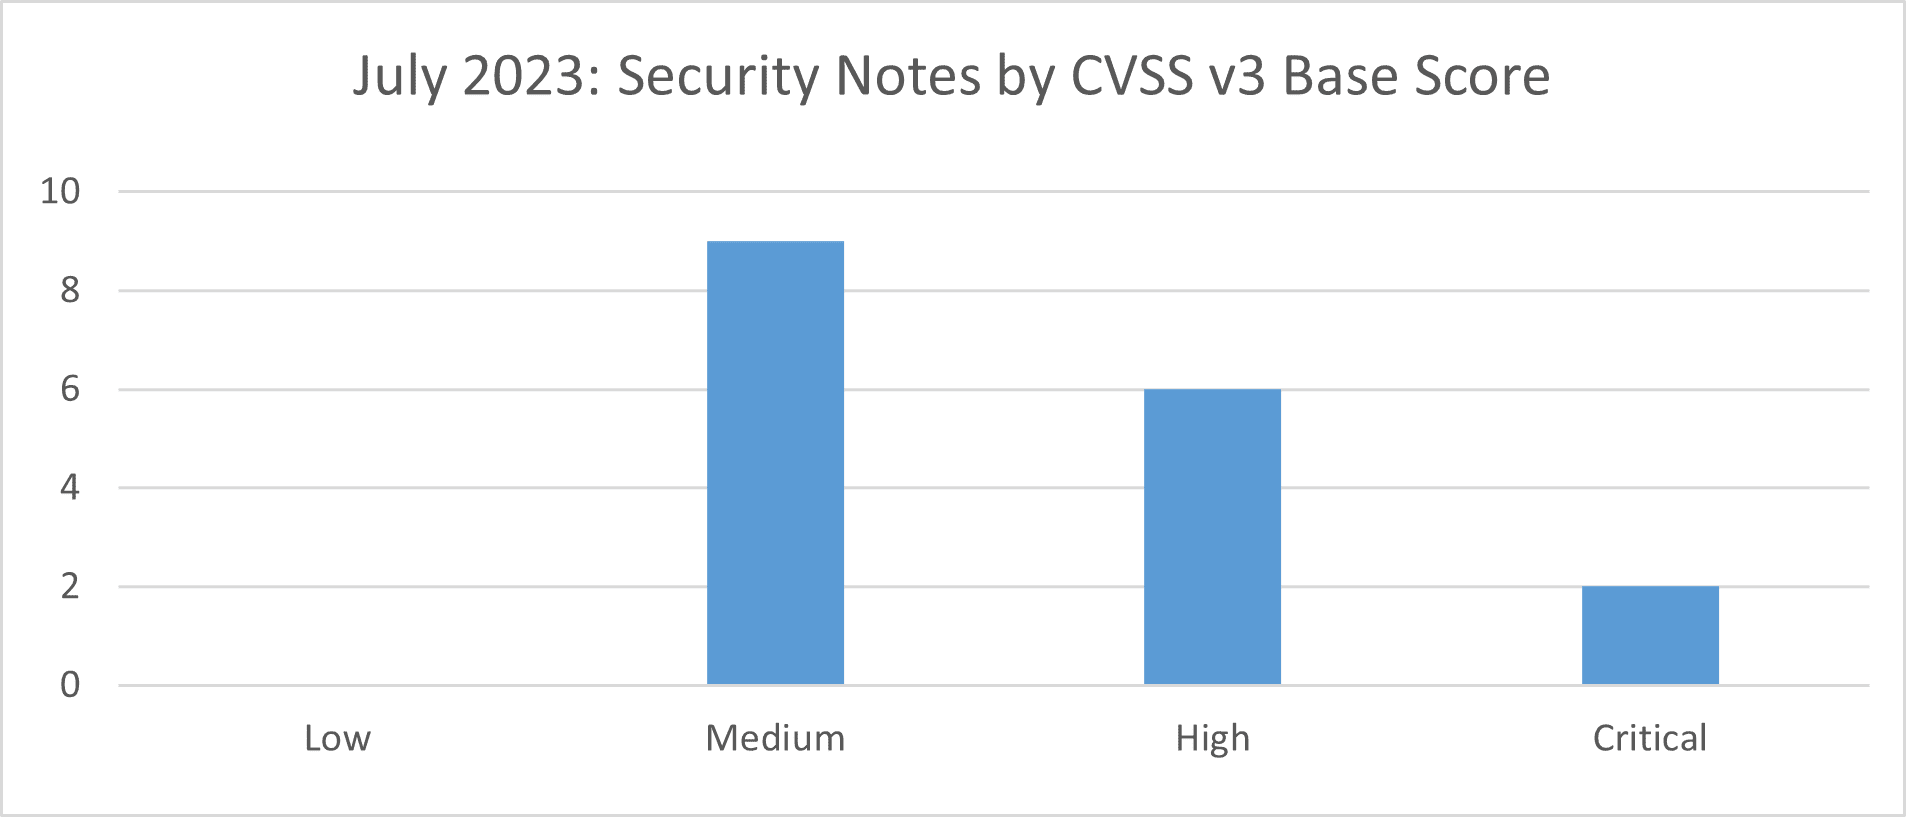
SAP’s security patch day for July 2023 has seen the release of 17 new OSS SAP security notes. Two notes have been classified as critical, six as high and nine as medium, based on CVSS v3.0 Rating.
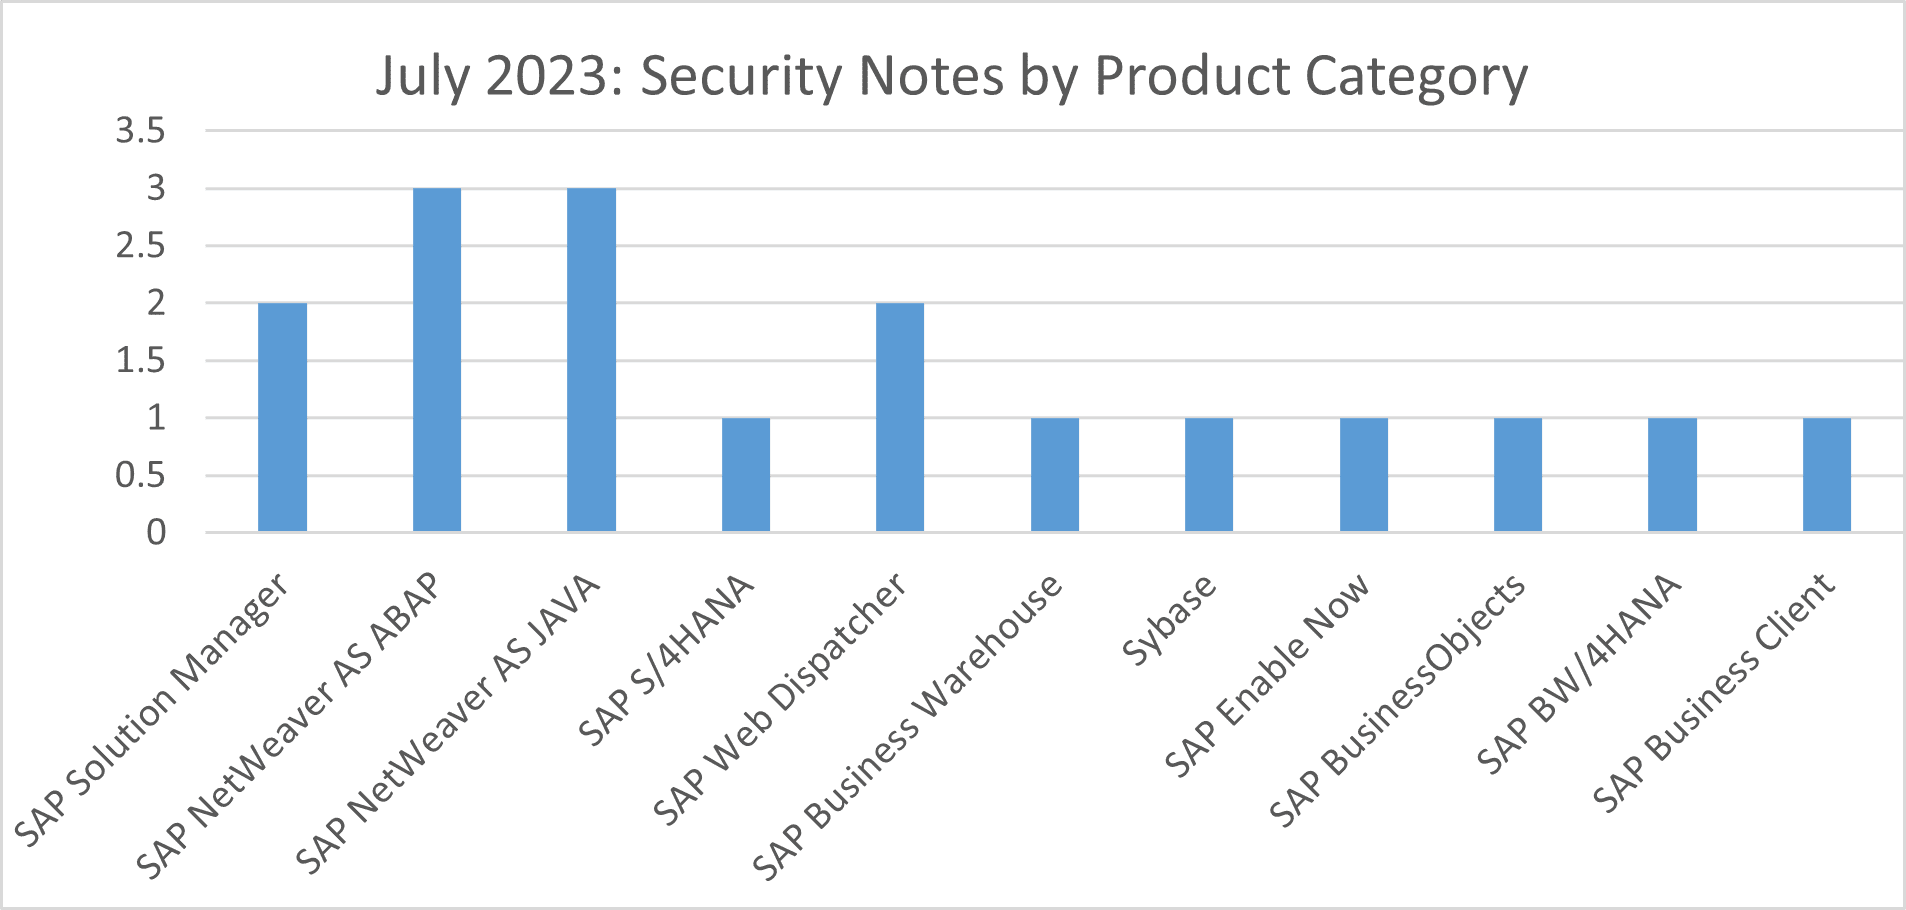
Three notes have been released for SAP NetWeaver AS JAVA and SAP AS NetWeaver AS ABAP. Two notes for SAP Solution Manager and SAP Web Dispatcher. Single notes have been released for SAP S/4HANA, SAP Web Dispatcher, SAP Business Warehouse, Sybase, SAP Enable Now, SAP BusinessObjects, SAP BW/4HANA and SAP Business Client.
Vulnerabilities: July 2023 Highlights
[CVE-2023-36922] OS command injection vulnerability in SAP ECC and SAP S/4HANA (IS-OIL) (SAP Note 3350297)
Due to a programming error in a function module and report, the IS-OIL component in SAP ECC and SAP S/4HANAallows an authenticated attacker to inject an arbitrary operating system command. Once successful exploited, the attacker can read or modify the system data and shut down the system.
[CVE-2023-36925] Unauthenticated blind SSRF in SAP Solution Manager (Diagnostics agent) (SAP Note 3352058)
SAP Solution Manager (Diagnostics agent) allows an unauthenticated attacker to execute HTTP requests blindly. On successful exploitation, the attacker can cause a limited impact on the confidentiality and availability of the application and other applications the Diagnostics Agent can reach.
[CVE-2023-35871] Memory Corruption vulnerability in SAP Web Dispatcher (SAP Note 3340735)
The SAP Web Dispatcher has a vulnerability, thus allowing an unauthenticated attacker to corrupt memory through logical errors in memory management. This may lead to information disclosure or system crashes as a result.
[CVE-2023-33989] Directory Traversal vulnerability in SAP NetWeaver (BI CONT ADD ON) (SAP Note 3331376)
Due to a directory traversal flaw, an attacker with non-administrative authorizations can overwrite system files. Data from confidential files cannot be read, but potentially some OS files can be over-written, leading to system compromise.